
Email looks immediate to users, but an Internet email may pass through an application, a submission server, one or more relays, DNS routing, queues, and recipient policies. Simple Mail Transfer Protocol (SMTP) coordinates the sending and relaying part of that journey. It does not decide whether a signup is genuine, whether a form submission came from a bot, or whether a recipient trusts the sender. Those decisions sit in security and operational controls around the transport path.
For platform and security teams, that distinction matters. A reliable email workflow needs both a correctly configured SMTP layer and safeguards for the web or application events that trigger messages. Understanding where each control belongs makes failures easier to diagnose and helps prevent an abused form, fake-account campaign, or compromised credential from becoming a downstream email incident.
What SMTP does in a modern email workflow
SMTP is an application-layer protocol for sending and relaying email. A mail client or application submits a message to an SMTP server; one or more mail transfer agents then relay it toward the recipient’s domain. The receiving system accepts, rejects, defers, or filters the message according to its own policies.
The protocol’s core behavior is standardized in RFC 5321. Modern deployments also use Extended SMTP (ESMTP), which lets servers advertise features such as authentication and supported message sizes after an EHLO command.
SMTP is often confused with inbox-access protocols. The division is simple:
- SMTP sends and relays messages.
- IMAP synchronizes mail stored on a server across clients.
- POP3 downloads messages from a server, commonly for local storage.
SMTP still underpins transactional alerts, password-reset messages, account confirmations, receipts, support notifications, and marketing mail. What changes from one environment to another is not the protocol’s basic purpose but who operates the relay, how the session is secured, and which controls protect the events that generate email.
How an SMTP message travels from application to inbox

An SMTP transaction can be reduced to five operational steps:
- An application or mail user agent creates the message and submits it to an outgoing server.
- The outbound mail transfer agent or relay responsible for the next hop identifies the recipient domain and, when direct delivery is required, looks up its mail exchange (MX) records in DNS.
- The sender opens an SMTP session with the next relay or recipient server and issues envelope commands such as
MAIL FROM,RCPT TO, andDATA. - The receiving server evaluates the connection, sender identity, policy, content, and reputation signals before accepting, deferring, or rejecting the message.
- If delivery cannot complete immediately, the sending system may queue the message and apply a retry policy. A permanent failure can appear as a synchronous
5xxreply; if a server already accepted the message and delivery later fails, the mail system can generate a delivery status notification.
The transport path moves the message; identity, policy, reputation, and abuse controls determine how safely the workflow operates.
1. The transport path
The SMTP envelope controls routing. It contains the return path and recipient commands used during the session. The visible From, To, and Subject fields belong to the message content and do not necessarily match the envelope. That separation is useful for legitimate forwarding and list operations, but it is also why authentication and policy checks cannot rely on a visible address alone.
For application-generated mail, the first hop is usually message submission rather than open server-to-server relay. RFC 6409 separates submission responsibilities from relay behavior and reserves port 587 for message submission. This helps teams apply authentication, policy, and correction rules at a controlled boundary.
2. Where delivery decisions happen
The sending relay controls authentication, queues, retries, routing, and outbound throttling. The recipient-side mail system applies acceptance policy, spam and malware filtering, domain-authentication checks, and mailbox-placement decisions. Responsibility transfers only after the receiving server returns a final 2xx reply following the end of message data; earlier successful replies do not guarantee acceptance of the complete message, and acceptance does not guarantee placement in the primary inbox.
Operational troubleshooting should therefore start by identifying the failed layer: application submission, relay authentication, DNS routing, connection/TLS, recipient policy, or post-acceptance filtering. Treating every failure as “SMTP is down” hides the evidence needed to fix it.
SMTP ports, commands, authentication, and encryption
Port numbers describe the expected connection role, not a universal security ranking.
| Port | Typical role | Security posture | Operational note |
|---|---|---|---|
| 25 | Server-to-server relay | STARTTLS may be negotiated | Common for MX-to-MX delivery; often restricted for client or cloud egress |
| 465 | Message submission with implicit TLS | Encryption begins when the connection opens | Supported by many modern providers and clients |
| 587 | Authenticated message submission | Usually STARTTLS plus SMTP-AUTH | Standard choice for applications and user agents submitting mail |
| 2525 | Provider-specific alternative submission | Depends on provider configuration | Useful when networks block standard submission ports, but not an IETF-assigned SMTP service port |
1. Choosing a submission or relay port
Applications should follow the relay provider’s documented submission settings rather than choose a port only because it is reachable. Port 25 usually belongs to server relay. Ports 465 and 587 are used for authenticated submission, with different TLS startup behavior. The organization must also verify firewall rules, credential storage, allowed sender identities, throttling, and timeout behavior.
2. Securing the session
SMTP-AUTH lets a submission server authenticate the client. STARTTLS upgrades an existing connection to TLS, while implicit TLS protects the connection from its first byte. RFC 8314 favors implicit TLS for message submission and access, while port 587 with STARTTLS remains widely deployed. In either case, applications should follow the provider’s documented TLS configuration and avoid cleartext credentials or content.
Encryption protects a connection in transit; it does not prove that the message itself is legitimate. Teams still need sender-domain authentication, credential controls, rate limits, and monitoring. A stolen SMTP credential can send abusive mail over a perfectly encrypted session.
SMTP security: identity, reputation, and abuse controls
SMTP was designed to transfer messages between cooperating systems. Modern email security adds several control layers around it:
- SPF, standardized in RFC 7208, authorizes sending hosts for an envelope
MAIL FROMorHELOidentity; it does not directly validate the visible From address. - DKIM, defined in RFC 6376, adds a cryptographic signature that receivers verify against the signing domain in the signature’s
d=tag, which is not necessarily the visible From domain. - DMARC, specified in RFC 7489, evaluates whether the visible From domain aligns with an authenticated SPF or DKIM domain and adds policy and reporting signals.
- TLS and SMTP-AUTH protect and authenticate submission sessions.
- Rate limits and quotas constrain bursts, compromised accounts, and unexpected application behavior.
- Bounce and complaint monitoring reveal invalid addresses, reputation problems, and abnormal sending patterns.
- List and form hygiene reduces messages generated from fake, mistyped, or malicious input.
These controls solve different problems. SPF, DKIM, and DMARC support domain identity and policy; they do not determine whether the web form that created a recipient record was filled by a real user. Conversely, bot protection at a signup form cannot replace SMTP authentication or domain policy. Mature systems assign each control to the layer where it has the strongest evidence.
Security teams should also protect the credentials and APIs that can trigger email. Use scoped credentials, rotate secrets, separate environments, restrict sender identities, and alert on volume or recipient-pattern changes. When an account or API key is compromised, the objective is to contain the sending path before reputation damage expands.
Self-hosted SMTP or managed relay?
The choice is primarily an operations decision.
| Decision area | Self-hosted SMTP | Managed relay |
|---|---|---|
| Control | Full control over software, queue, routing, and data path | Configuration within provider capabilities and policies |
| Operations | Team owns patching, deliverability, reputation, scaling, and incident response | Provider operates core relay infrastructure; customer still owns configuration and content practices |
| Observability | Fully customizable, but must be built and maintained | Dashboards, logs, webhooks, and suppression tools are commonly provided |
| Scaling | Requires capacity planning and queue management | Designed to absorb variable volume within service limits |
| Governance | Easier to tailor for strict internal architecture | May simplify operations, but privacy, data location, and vendor review remain necessary |
1. When self-hosting is justified
Self-hosting can make sense when an organization has experienced mail administrators, strict network or data-path requirements, and a clear reason to own the full relay stack. It also requires continuous attention to DNS, certificates, patching, queue health, abuse response, IP and domain reputation, feedback loops, and recipient-specific policy changes.
2. When a managed relay is safer
A managed relay can reduce infrastructure work and provide established tooling for authentication, retries, suppression, analytics, and escalation. It does not transfer all responsibility to the provider. The application owner still controls recipient consent, message triggers, credential security, rate policies, and the quality of upstream data.
Whichever model is chosen, document where responsibility changes hands: application owner, submission service, outbound relay, DNS owner, managed provider, and recipient-side operator. That map is more useful during an incident than a generic assumption that one vendor owns the entire path.
Where bot and form-abuse prevention fits around SMTP
Bot and form abuse happens before SMTP, but its consequences arrive in the mail system. Public signup, reset, contact, referral, and subscription flows can generate validly formatted yet unwanted messages. Application controls decide whether an action should trigger mail; SMTP then submits or relays the approved message.
The main abuse patterns and their SMTP-side effects are:
- Fake signups: scripts create accounts and generate verification or onboarding mail, increasing queue and sender-reputation pressure.
- Reset or notification bombing: repeated requests send unwanted mail to one person or domain, leading to complaints, throttling, and support tickets.
- Contact and referral spam: fabricated data pollutes CRM or support workflows and can trigger follow-ups that recipients never requested.
- Credential and account automation: scripted login or recovery attempts create bursts of alerts, resets, and other security notifications.
The fix should match the trigger. Put server-side validation, rate limits, quotas, cooldowns, request deduplication, and neutral responses around the endpoint. Use account, device, IP, frequency, and recipient-pattern signals to separate normal activity from coordinated abuse. An effective bot detection solution can support that decision; device fingerprinting adds continuity when automation rotates accounts or network addresses. Challenge only higher-risk requests so ordinary users avoid unnecessary friction.
GeeTest fits at this upstream decision point. Adaptive CAPTCHA can verify a suspicious signup, reset, or form submission, while Device Fingerprinting contributes device-level risk signals. Where policies differ by account state, action, or business threshold, the Business Rules Engine can help orchestrate the decision. These capabilities support fraud prevention around email-triggering workflows; they do not provide SMTP relay, SPF, DKIM, DMARC, TLS, or mailbox delivery.
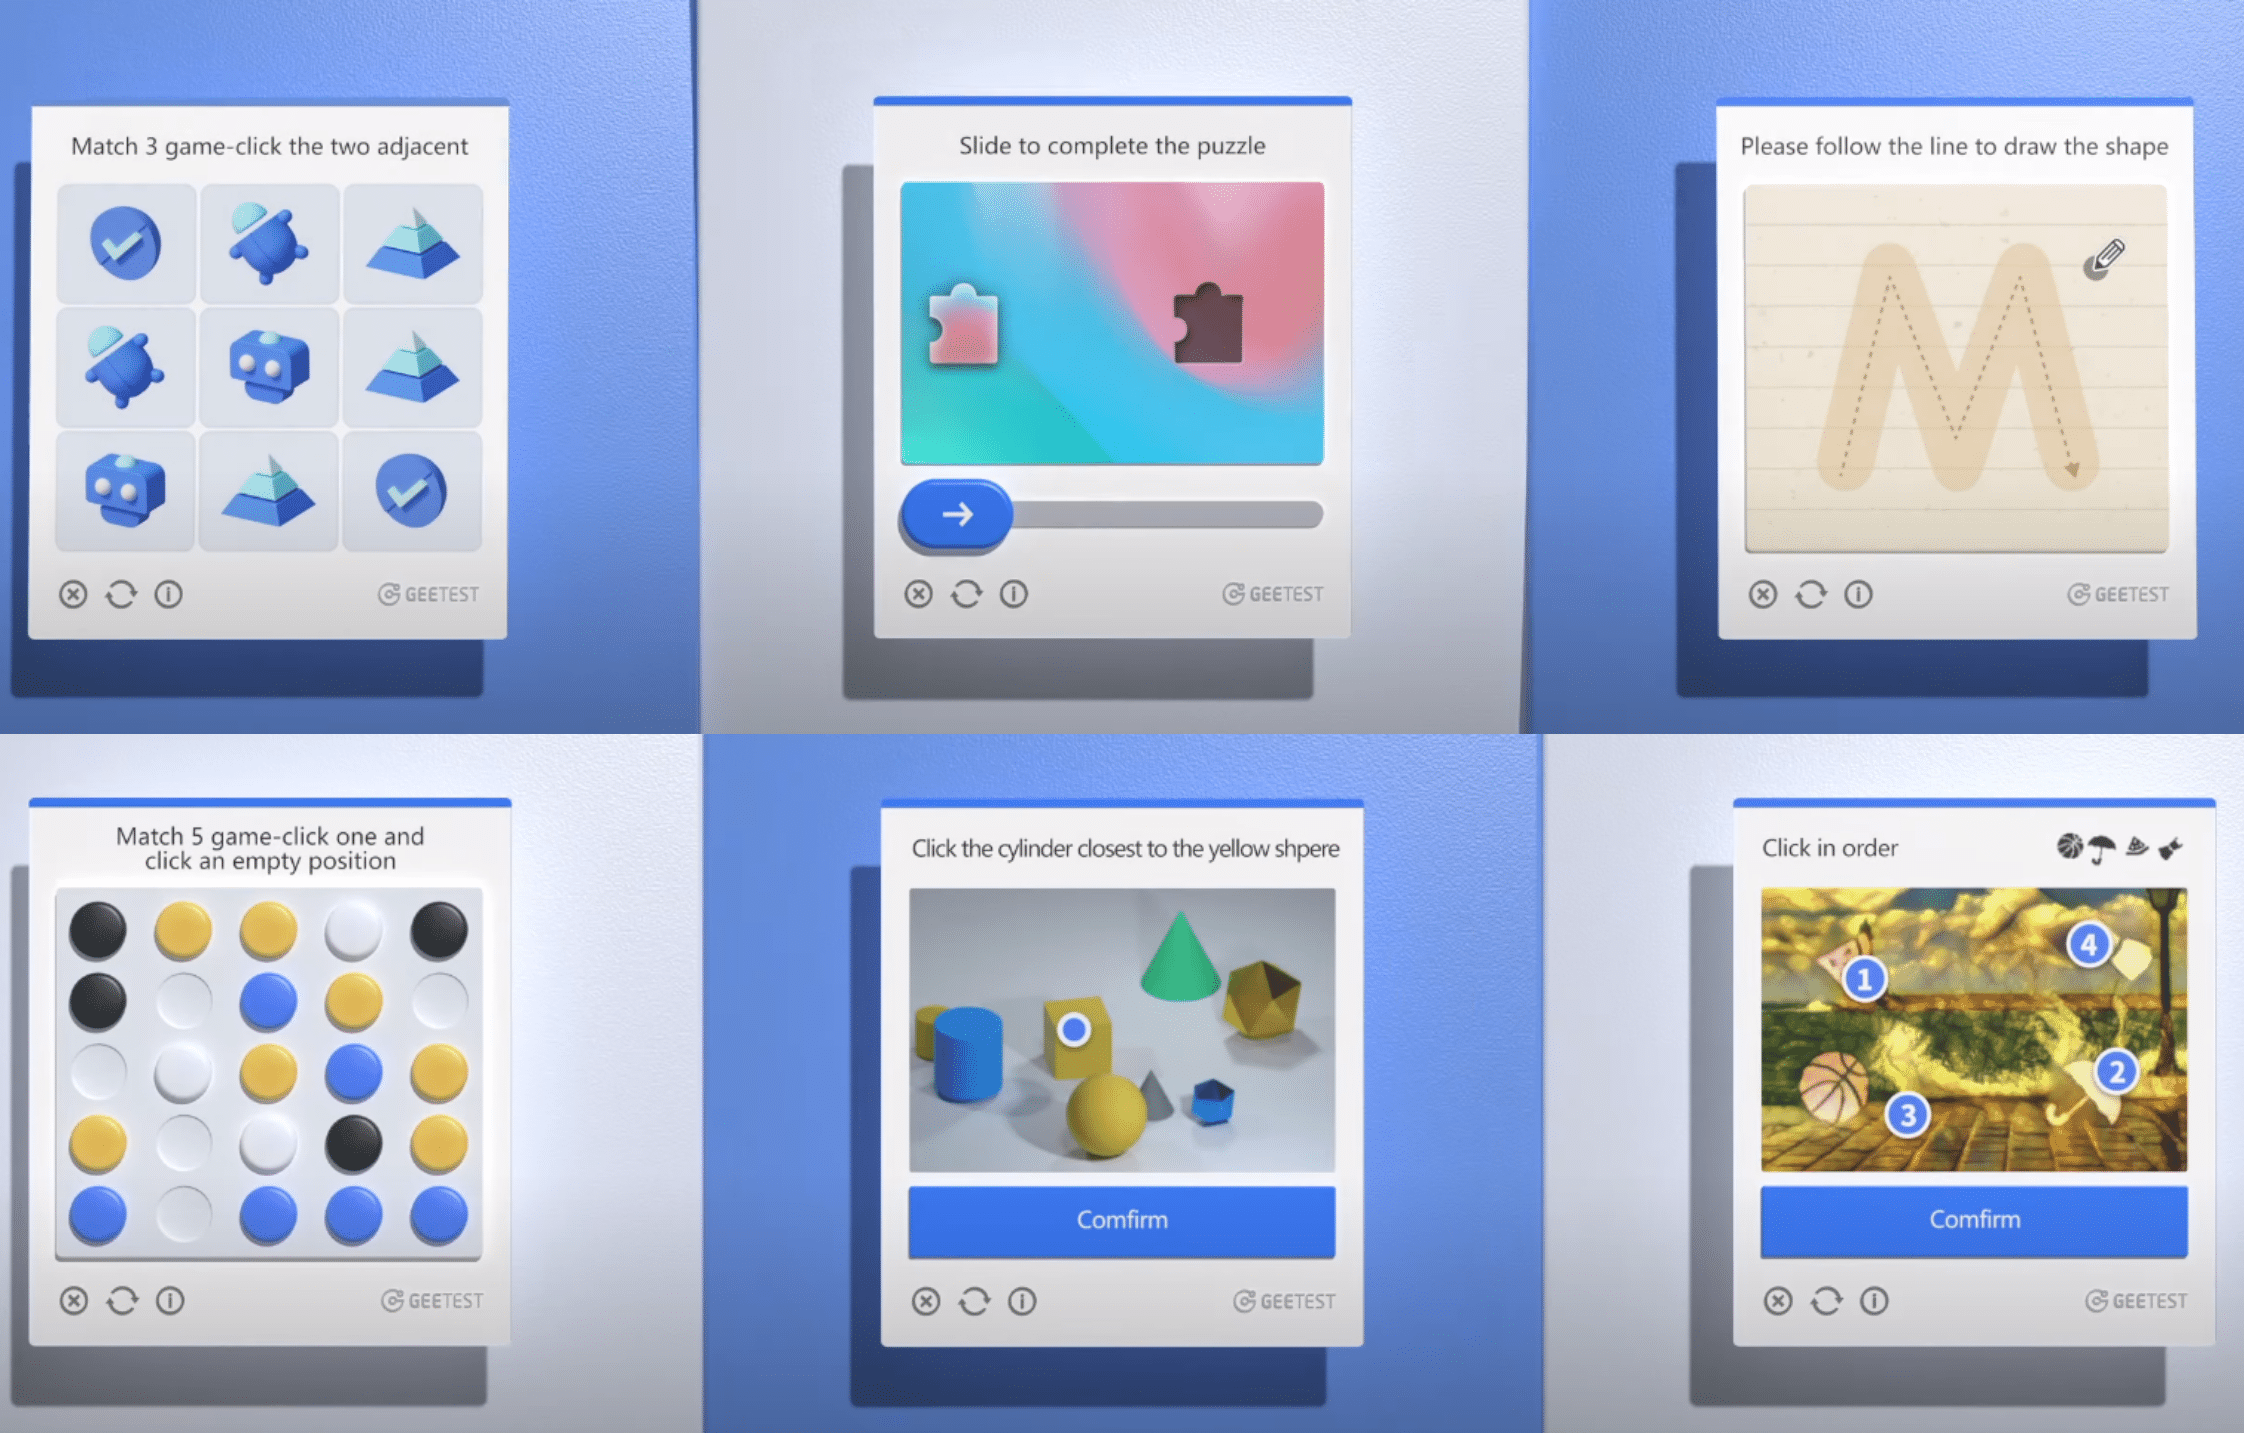
Adaptive verification belongs before the email request reaches SMTP. It is an application-layer control, not part of SMTP transport or sender authentication.
Practical SMTP checklist and final takeaway
Use the following controls to close the gap between an abused trigger and the SMTP layer:
- For fake accounts and form bots: validate inputs on the server, cap actions by account/device/IP, and place form-spam controls at public entry points. Use GeeTest Adaptive CAPTCHA as a risk-based step-up rather than a blanket challenge.
- For reset and notification bombing: add cooldowns, deduplicate repeated requests, cap recipient and account frequency, and return a neutral response that does not reveal account state. Device Fingerprinting can add continuity to the risk decision.
- For coordinated multi-signal abuse: combine device, account, IP, velocity, and action context. GeeTest’s Business Rules Engine can help teams apply differentiated policies instead of one global threshold.
- For SMTP credential compromise: scope and rotate secrets, monitor authentication failures, set outbound quotas, and rehearse revocation. These are messaging and security controls, not a CAPTCHA function.
- For legitimate users: keep verification selective, measure challenge and recovery outcomes, and define a fallback when a control or relay is unavailable.
- For operations: document the application, relay path, DNS/authentication owners, recipient domains, queue limits, complaint signals, and escalation path. Review security protocol and account takeover controls alongside the mail runbook.
The takeaway is simple: SMTP should transport legitimate messages, while the application decides which human-facing actions deserve to create them. If unwanted email is rising, reduce abusive signup, reset, and form requests before expanding relay capacity. GeeTest can help evaluate risk signals and step-up verification at those entry points; SMTP relay, sender authentication, and mailbox delivery remain separate responsibilities.
1. What is SMTP in email?
SMTP, or Simple Mail Transfer Protocol, is the standard used to submit, send, and relay email. A client or application gives a message to an SMTP server, which routes it toward the recipient’s mail server. Inbox retrieval is handled by protocols such as IMAP or POP3.
2. How do I find my SMTP server?
Check the configuration supplied by your email or relay provider. You normally need a server hostname, submission port, TLS mode, username or credential, and allowed sender identity. Do not infer the submission server only from a domain’s MX record; MX records identify inbound destinations, not necessarily the correct client-submission endpoint.
3. Is SMTP still used?
Yes. SMTP remains the standard transport for sending and relaying Internet email. Modern systems extend it with authentication, TLS, domain-identity controls, queues, provider APIs, and monitoring. Some applications submit mail through an HTTP API, but the provider typically uses SMTP within the wider delivery path.
4. Does SMTP use port 25 or 587?
Both, for different roles. Port 25 is primarily used for server-to-server relay. Port 587 is the standard message-submission port for authenticated clients and applications, usually with STARTTLS. Port 465 is also widely used for submission with implicit TLS. Follow the service provider’s documented configuration.
5. How is SMTP different from IMAP and POP3?
SMTP sends and relays mail. IMAP lets clients synchronize messages and folders stored on a mail server. POP3 downloads messages, often for local access. In a typical workflow, SMTP handles the outbound path while IMAP or POP3 handles the user’s inbox-access path.